AI
L1 SOC Automation
AI agents execute initial alert analysis, triage, investigation, and other repetitive L1 activity. Escalations reach L2 with context, so analyst time is reserved for complex investigations, threat analysis, and decisions.
Loading...
AI SOC AUTOMATION
Cywarden automates routine L1 SOC operations with AI agents. Initial alert analysis, triage, and repetitive investigation are completed before escalation, so L2 analysts focus on complex investigations, threat analysis, and response decisions.
The Challenge
Round-the-clock alert volume outpaces hiring. Analysts spend shifts on initial analysis, triage, and repetitive investigation while higher-severity cases wait. AI agents take that L1 workload so L2 capacity stays on complex investigations and the rest of the security program.
How Cywarden addresses this
AI agents for L1 analysis
L1 triage at volume
Escalation to L2 analysts
What We Deliver
L1 automation is the operating model. AI agents absorb routine SOC workload, while cloud security, compliance, and the broader program continue under the same engagement. The result is faster detection, lower residual risk, and sustained compliance, at a volume a manual L1 queue cannot hold.
AI agents execute initial alert analysis, triage, investigation, and other repetitive L1 activity. Escalations reach L2 with context, so analyst time is reserved for complex investigations, threat analysis, and decisions.
24/7 monitoring, investigation, and containment from a global SOC. AI agents clear routine L1 analysis and triage, so escalation, complex cases, and response remain with analysts.
Continuous visibility across AWS, Azure, and GCP. We secure your cloud identity fabric, enforce least-privilege access, and eliminate misconfigurations that lead to breaches.
Enterprise risk assessments, treatment planning, and board-ready reporting that translate technical exposure into business decisions.
End-to-end support for ISO 27001, SOC 2 Type I/II, GDPR, and NIST with automated evidence collection and year-round audit readiness.
Deployment of modern governance, risk, and compliance platforms like Vanta, Drata, ServiceNow GRC, and OneTrust.
AI agents automate initial alert analysis, triage, and repetitive investigation. L2 analysts recover that time for complex cases, threat analysis, and decisions. Cloud security and compliance are part of the same engagement.
Book a Security ConsultationOur Approach
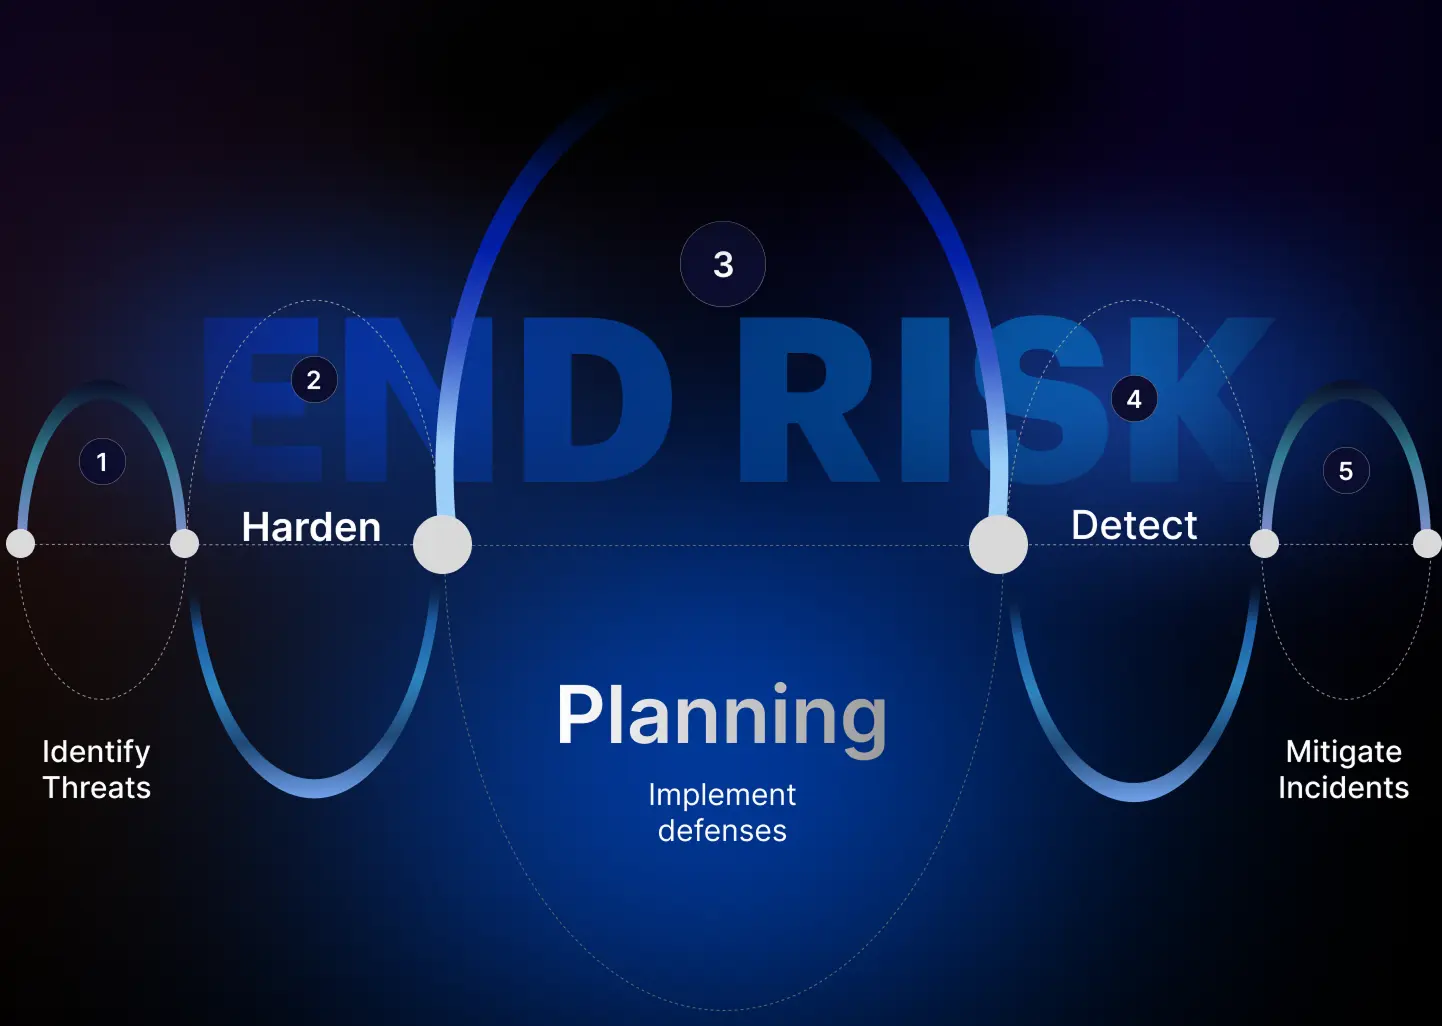
We use a battle-tested approach that enables organizations to transition from reactive security to enduring, governance-aligned resilience. Each engagement is tailored to your business context, industry regulations, and level of operational maturity.
Full review of your security posture, threats, and compliance obligations, with a gap analysis against NIST CSF and ISO 27001 leading to a prioritized roadmap.
Target-state architecture, policies, and controls built for your environment, with every control mapped to a defined business risk.
We deploy controls, monitoring, and automated evidence collection, then work alongside your team until operations are running.
Audit readiness and continuous compliance, with governance that adapts as threats and regulations change.
Business Impact
Impact is measured in L1 workload removed from the queue, analyst time returned to L2, and risk reduced across the security program.
When compliance and security operate together, the downstream effects are tangible: fewer audit surprises, stronger vendor trust, faster deal cycles where security questionnaires are a formality rather than a blocker, and the ability to enter regulated markets with confidence.
Reduction in routine L1 workload once agents assume analysis, triage, and investigation
Faster alert-to-decision cycle versus manual L1 triage
Less engineering time spent on compliance evidence and audit preparation
Certification success rate across ISO 27001, SOC 2, and GDPR engagements
What leaders are saying
Executive voices from organizations that have worked with Cywarden to transform their security operations.
We brought Cywarden in to close a SOC 2 gap that was blocking a major enterprise deal. They did not just get us certified they rebuilt how we think about compliance. Evidence collection that used to take weeks now runs automatically. Our sales cycle shortened by a full quarter.
VP of Engineering
Series C SaaS Company Healthcare Vertical
Before Cywarden, our board received a quarterly security report that nobody fully understood. Now we have real-time risk visibility, clear metrics, and a governance framework that lets me answer the hard questions with confidence. They changed how the business sees security.
CISO
Global Financial Services Firm 4,000+ Employees
We evaluated three managed security providers. Cywarden was the only one that started with our business risks instead of their product catalog. Their team embedded with ours, understood our multi-cloud complexity, and delivered measurable improvements within 90 days.
CIO
Enterprise Software Provider - North America
Our cloud environment expanded rapidly across AWS and Google Cloud, and security governance struggled to keep pace. Cywarden provided the visibility, automation, and expertise we needed to secure our infrastructure at scale. Their guidance enabled us to pass multiple customer security assessments with zero findings.
VP of Infrastructure & Cloud Operations
Enterprise Manufacturing US and APAC Operations
What impressed us most was Cywarden's ability to translate cybersecurity risk into business language. Their executive reporting gave our leadership team a clear understanding of where investments were needed and how those investments reduced risk. That level of transparency was invaluable.
Chief Risk Officer
Regional Banking Institution
Google Cloud was central to our growth strategy, but securing a rapidly expanding environment across multiple business units had become increasingly complex. Cywarden helped us establish a comprehensive Google Cloud security framework, implement continuous monitoring, and strengthen identity and access controls. Within months, we achieved greater visibility, reduced risk exposure, and gained the confidence to scale our cloud operations securely.
Head of Cloud Infrastructure
Global Technology Services Company - Google Cloud Environment
We brought Cywarden in to close a SOC 2 gap that was blocking a major enterprise deal. They did not just get us certified they rebuilt how we think about compliance. Evidence collection that used to take weeks now runs automatically. Our sales cycle shortened by a full quarter.
VP of Engineering
Series C SaaS Company Healthcare Vertical
Before Cywarden, our board received a quarterly security report that nobody fully understood. Now we have real-time risk visibility, clear metrics, and a governance framework that lets me answer the hard questions with confidence. They changed how the business sees security.
CISO
Global Financial Services Firm 4,000+ Employees
We evaluated three managed security providers. Cywarden was the only one that started with our business risks instead of their product catalog. Their team embedded with ours, understood our multi-cloud complexity, and delivered measurable improvements within 90 days.
CIO
Enterprise Software Provider - North America
Our cloud environment expanded rapidly across AWS and Google Cloud, and security governance struggled to keep pace. Cywarden provided the visibility, automation, and expertise we needed to secure our infrastructure at scale. Their guidance enabled us to pass multiple customer security assessments with zero findings.
VP of Infrastructure & Cloud Operations
Enterprise Manufacturing US and APAC Operations
What impressed us most was Cywarden's ability to translate cybersecurity risk into business language. Their executive reporting gave our leadership team a clear understanding of where investments were needed and how those investments reduced risk. That level of transparency was invaluable.
Chief Risk Officer
Regional Banking Institution
Google Cloud was central to our growth strategy, but securing a rapidly expanding environment across multiple business units had become increasingly complex. Cywarden helped us establish a comprehensive Google Cloud security framework, implement continuous monitoring, and strengthen identity and access controls. Within months, we achieved greater visibility, reduced risk exposure, and gained the confidence to scale our cloud operations securely.
Head of Cloud Infrastructure
Global Technology Services Company - Google Cloud Environment
Why Cywarden
Security programs are governed, measured, and aligned to business risk. AI agents carry routine L1 SOC work. L2 analysts own complex investigations, threat analysis, and decisions, with cloud, compliance, and governance delivered by the same team.
Operations across the US, Europe, and APAC with regional expertise in regulatory requirements, data residency, and cultural expectations. We scale with you, wherever you operate.
Initial alert analysis, triage, and repetitive investigation run on AI agents. L2 analysts retain complex investigations, threat analysis, and the decision to contain or escalate. The same practitioners deliver cloud security, compliance, and governance.
Every control we implement maps to a risk. Every process aligns with recognized frameworks. We build security programs that survive leadership changes, audits, and board scrutiny.
CISA, CISM, ISO Lead Auditor, and cloud-native security certifications across our team. We embed senior practitioners with your organization - not junior analysts behind a dashboard.
We deploy the platforms that fit your scale and maturity - not the vendor that pays us the highest margin. Your stack should serve your security goals, not the other way around.
Our engagements do not end at delivery. We operate as a continuous extension of your team - adapting to new threats, evolving compliance requirements, and shifting business priorities.
AI agents remove routine alert analysis, triage, and investigation from the L1 queue. L2 analysts apply that capacity to complex threats and response decisions. Cloud security and compliance are delivered alongside the SOC.
Book a Security Consultation